AI Release Management Expands to Behavioral and Temporal Governance
AI systems require release processes that track non-code components and temporal data integrity to prevent behavioral drift and look-ahead bias.

Published
September 10, 2026
Reading time
3 minutes
Perspective
Research
Topics
AI release engineering · behavioral monitoring · data leakage
Traditional software release engineering assumes reproducibility through versioned code artifacts. AI systems disrupt this model because behavior can change without code deployment—through model updates, prompt edits, retrieval index refreshes, or policy rule modifications. The HackerNoon article argues these components must be treated as release inputs, documented in a manifest to enable traceability. Separately, financial AI backtests face hidden risks when data timestamps or revisions introduce future information into past decision points, creating performance illusions that vanish under honest temporal constraints.
AI release artifacts must include non-code components
The source explicitly requires an AI release manifest to identify the application build, prompt version, model name and provider, retrieval data snapshot, tool schema, policy rules, evaluation suite, and fallback path. These are not metadata but essential inputs that determine production behavior. The article insists that treating prompts, models, or tool contracts as invisible runtime details creates unmanageable risk, and that the YAML structure is merely a vehicle for this principle—not the innovation itself.
Source: Release Engineering for AI Features: Rollouts, Rollbacks, and Runtime Risk · HackerNoon · AI
Financial AI backtests are vulnerable to temporal data leakage
The source explains that financial AI models can gain access to future information through revised datasets, delayed publication dates, or incorrect timestamps. A data point labeled March 2023 may have been published in April, yet still be used in a backtest as if it were available at decision time. This look-ahead bias creates performance illusions that vanish under honest temporal constraints. The article cites a 2026 preprint showing that minor timing violations materially improve backtest results, demonstrating that models may exploit flawed experiments rather than genuine market patterns.
Source: How Trading AI Can Accidentally See the Future — and How to Prevent It · HackerNoon · ML
Evo AI system tracks relationship development, not just facts
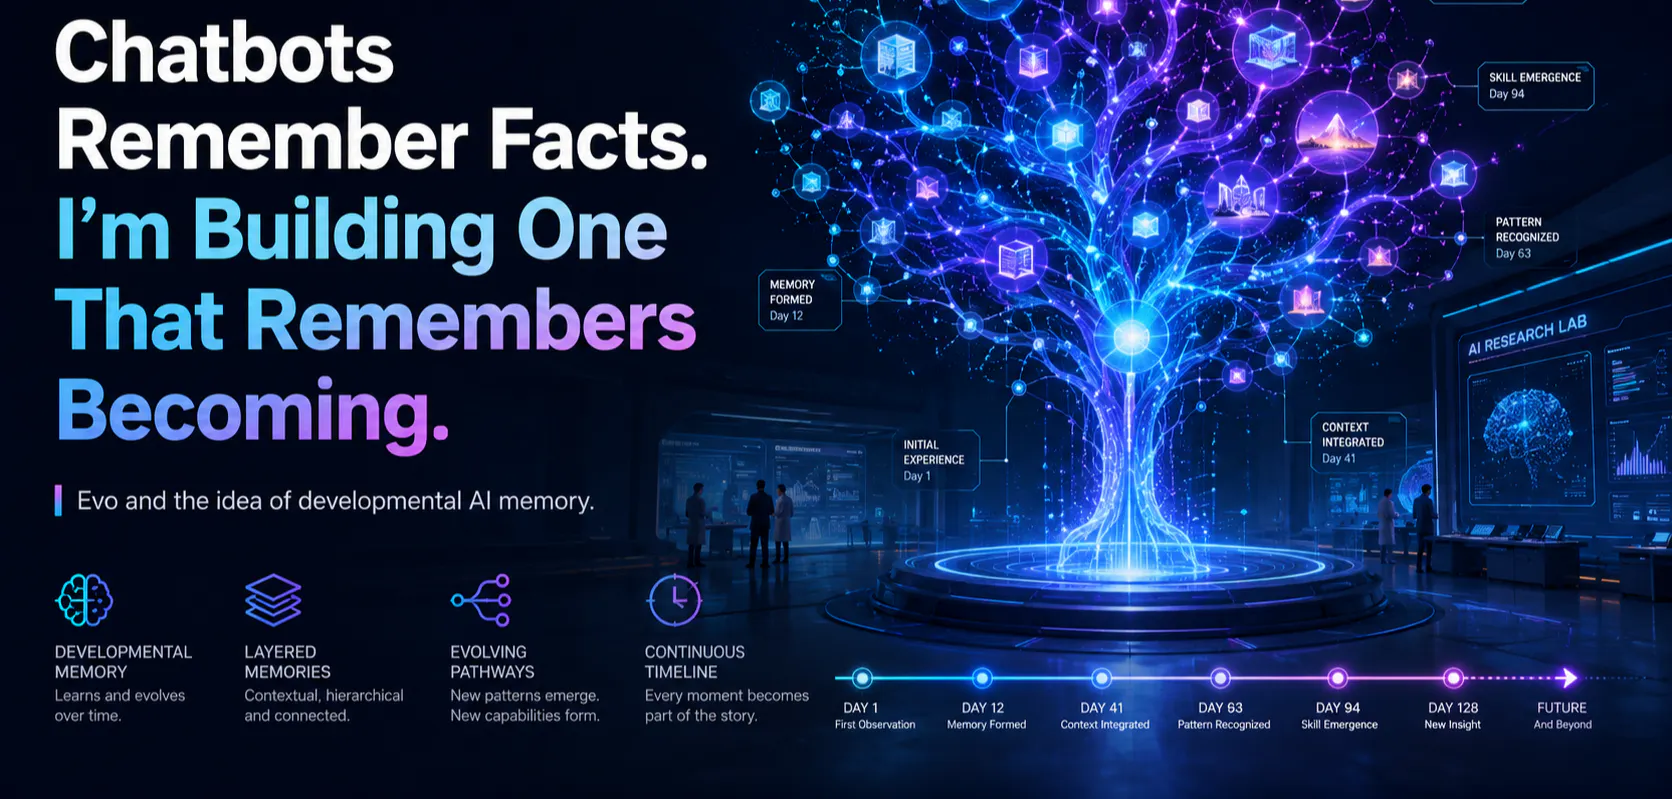
The source describes Evo as an experimental AI companion that preserves a developmental history of interactions, including changing preferences, emerging boundaries, uncertainty shifts, and relationship evolution over time. Unlike traditional memory systems that store facts like favorite food or job title, Evo records how preferences formed, what events triggered changes, and how both human and AI perspectives evolved. The system’s conceptual schema includes fields like 'changes_over_time', 'previous_states', and 'unresolved_questions'—indicating a deliberate design to capture transformation, not static state.
Source: Chatbots Remember Facts. I’m Building One That Remembers Becoming · HackerNoon · AI
Geopolitical AI power now hinges on permission architecture
The source states that August 2026 revealed AI power is increasingly determined by control over conversion interfaces—model release approvals, compute access, grid connections, data sovereignty, identity systems, and software provenance—not just model performance or chip inventory. The EU enforced market-access rules, Texas audited data-center interconnections, and the U.S. linked bulk-power security to AI growth. Nvidia H200s reached China under dual-permission regimes, and Ukraine-U.S. collaboration integrated battlefield data with model co-development. The article concludes that governance now controls whether assets become operational capability.
Source: August 2026 Reframed the Geopolitics of AI · HackerNoon · ML
What to watch next
The convergence of AI release complexity, temporal data integrity, developmental memory systems, and geopolitical permission layers reveals a broader trend: AI systems are no longer governed by static code or isolated models. Their behavior, safety, and strategic value are increasingly shaped by dynamic, multi-layered systems of control, traceability, and context. Each development underscores the need for precise, documented, and auditable governance across technical, temporal, and institutional dimensions.
Continue reading